.png)
How Continuous Pentesting Supports PCI DSS Compliance
Compliance Is No Longer Just About Passing an Audit
 ITSEC Asia
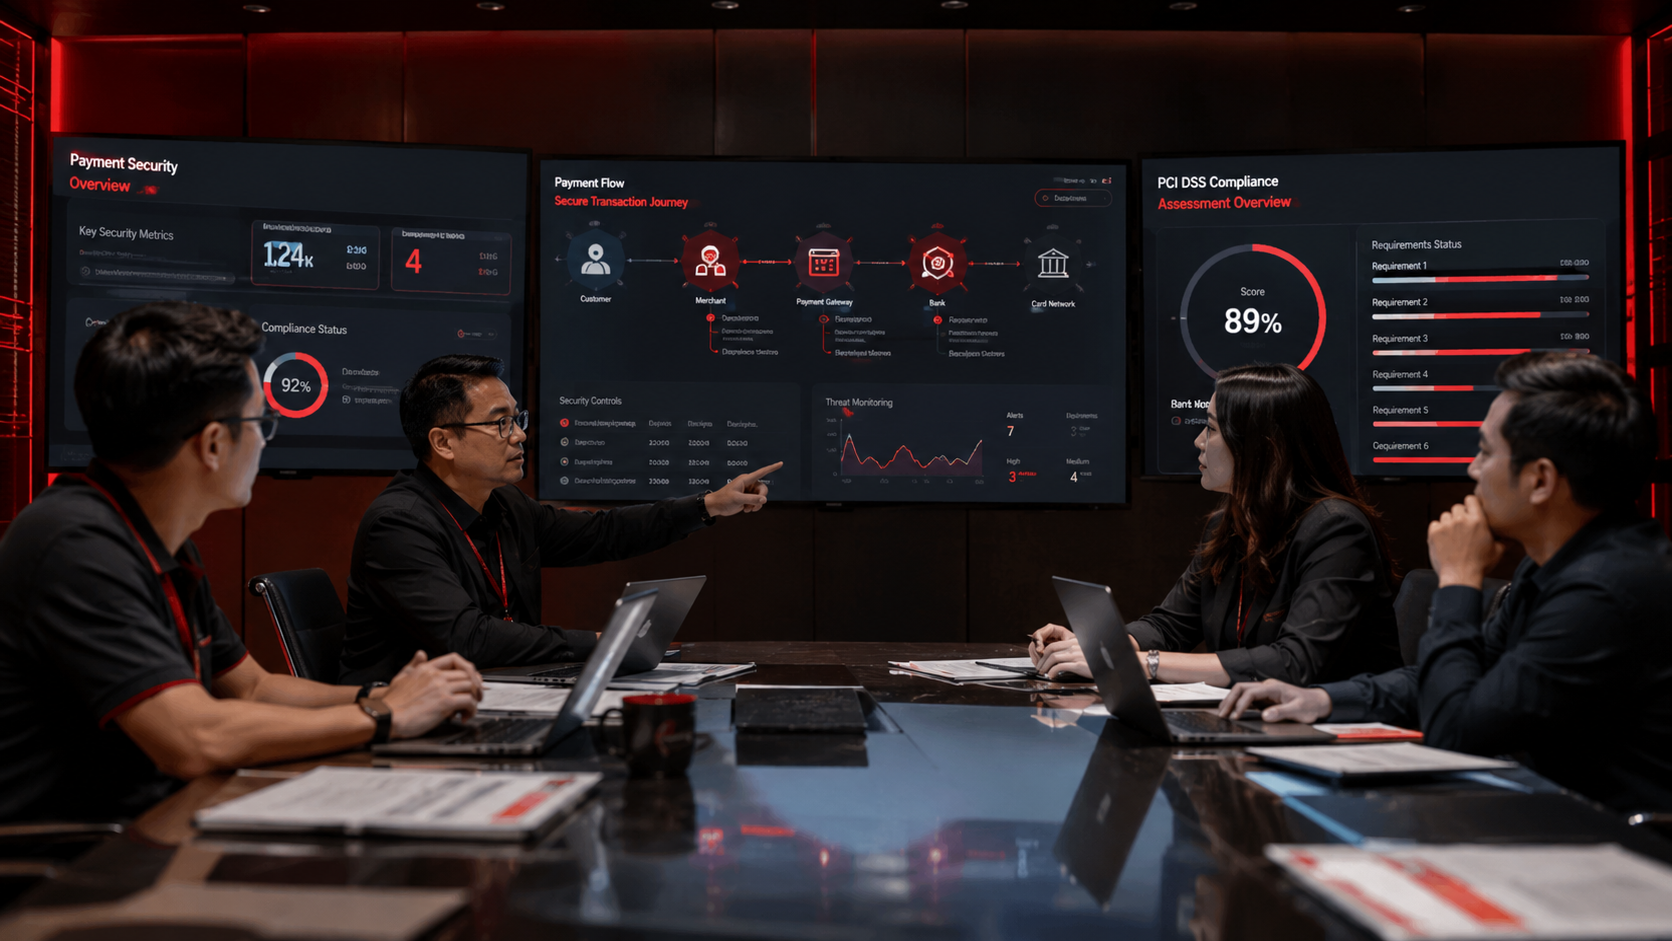
Organizations that process, store or transmit payment card information face increasing pressure to protect sensitive data and comply with industry standards.
Among the most widely recognized requirements is the Payment Card Industry Data Security Standard (PCI DSS).
While many organizations view PCI DSS as a compliance exercise, the reality is that the framework is designed to strengthen security and reduce the risk of data breaches.
As cyber threats continue to evolve, organizations are also recognizing that point-in-time assessments may no longer provide sufficient visibility.
This is where Continuous Pentesting and Continuous Security Validation can help.
What Is PCI DSS?
PCI DSS is a security framework developed to help organizations protect cardholder data and maintain secure payment environments.
It applies to merchants, financial institutions, payment processors and service providers that handle payment card information.
The standard covers multiple areas, including:
- Network security.
- Access control.
- Vulnerability management.
- Monitoring and logging.
- Security testing.
- Incident response.
The objective is not simply compliance but the protection of sensitive payment information.
Why Penetration Testing Matters for PCI DSS
Security testing plays a critical role within PCI DSS requirements.
Penetration testing helps organizations:
- Identify exploitable vulnerabilities.
- Validate security controls.
- Assess segmentation effectiveness.
- Understand attack paths.
- Reduce exposure to cyber threats.
Rather than relying solely on vulnerability scanning, PCI DSS recognizes the importance of simulating real-world attack scenarios.
This provides greater confidence that defenses are working as intended.
The Limitations of Periodic Assessments
Traditional penetration testing is often conducted annually or after significant changes to the environment.
However, modern infrastructures change continuously.
Organizations regularly:
- Deploy new applications.
- Modify cloud environments.
- Introduce new APIs.
- Add third-party integrations.
- Update systems and configurations.
As a result, risks can emerge long before the next scheduled assessment.
This creates gaps in visibility and potentially increases exposure.
What Is Continuous Pentesting?
Continuous Pentesting extends the principles of traditional penetration testing by introducing ongoing validation.
Rather than waiting months between engagements, organizations continuously evaluate changes in their environment and identify emerging risks.
Continuous Pentesting provides:
- Greater visibility.
- Faster feedback loops.
- Improved risk prioritization.
- Reduced blind spots.
- Stronger cyber resilience.
The objective is not to replace traditional penetration testing but to complement it.
How Continuous Pentesting Supports PCI DSS
Continuous Visibility Into Security Posture
Organizations gain greater awareness of changing risks and can address issues before they become audit findings.
Faster Identification of New Risks
New vulnerabilities and misconfigurations can be detected earlier, reducing the likelihood of exposure.
Improved Remediation Prioritization
Security teams can focus on issues that represent meaningful risks rather than treating every finding equally.
Better Audit Readiness
Continuous evidence and ongoing validation help organizations maintain stronger security documentation and demonstrate a proactive approach to compliance.
Enhanced Confidence in Security Controls
Rather than relying on assumptions, organizations can continuously verify whether controls remain effective over time.
Continuous Validation Complements Human Expertise
Compliance should never become a checkbox exercise.
Technology can improve speed and efficiency, but experienced professionals remain essential.
Human experts provide:
- Business context.
- Complex attack simulations.
- Segmentation validation.
- Strategic guidance.
- Interpretation of findings.
AI and automation help improve scale and visibility.
Human expertise ensures accuracy and meaningful insights.
Together, Human + AI create a stronger approach to compliance and offensive security.
PCI DSS 4.0 and the Shift Toward Continuous Security
PCI DSS 4.0 places greater emphasis on ongoing security practices and continuous risk management.
Organizations are increasingly expected to demonstrate that security controls remain effective over time rather than only during audits.
This shift aligns naturally with Continuous Security Validation.
Moving from periodic assessments toward continuous assurance helps organizations improve resilience while strengthening compliance efforts.
Conclusion
PCI DSS compliance is about more than passing audits.
It is about protecting payment card data and maintaining trust.
Traditional penetration testing remains essential, but modern environments require greater visibility and more proactive validation.
Continuous Pentesting helps organizations identify emerging risks faster, strengthen security controls and maintain a more sustainable approach to compliance.
As cyber threats continue to evolve, organizations that embrace continuous security practices will be better positioned to meet regulatory requirements and protect their customers.
Explore Bronyx
Bronyx is an AI-powered autonomous penetration testing platform developed by ITSEC Asia. Built around a Human + AI philosophy, Bronyx helps organizations continuously validate their security posture, reduce blind spots and improve visibility into evolving cyber risks.
By combining intelligent automation with human expertise, Bronyx enables organizations to move beyond point-in-time assessments and adopt a more sustainable approach to offensive security and compliance.
👉 Learn more about Bronyx: https://bronyx.ai
Need PCI DSS Penetration Testing Services?
Compliance requires more than automated scans.
Experienced cybersecurity professionals remain essential for validating segmentation controls, identifying complex attack paths and ensuring assessments align with PCI DSS requirements.
ITSEC Asia is a CREST-accredited cybersecurity company trusted by enterprises and government organizations across Southeast Asia. Our experts provide:
- PCI DSS Penetration Testing
- Vulnerability Assessments
- Web Application Security Testing
- API Security Testing
- Red Team Assessments
- Cybersecurity Consulting
Whether you are preparing for PCI DSS audits or strengthening your payment environment, ITSEC Asia can help you improve security and compliance.
👉 Explore ITSEC Asia's cybersecurity services: https://itsec.asia