.png)
Cybersecurity Training Is Only the Beginning
The real test of cybersecurity education is what people can do when they enter an organization, not simply what they know when they leave the classroom.
 ITSEC Asia
Cybersecurity training has a familiar finish line: the course ends, the certificate arrives and everyone takes a photograph. The harder question comes next. Can the graduate identify a suspicious event, explain its impact to a colleague and take the right action without making a bad situation worse?
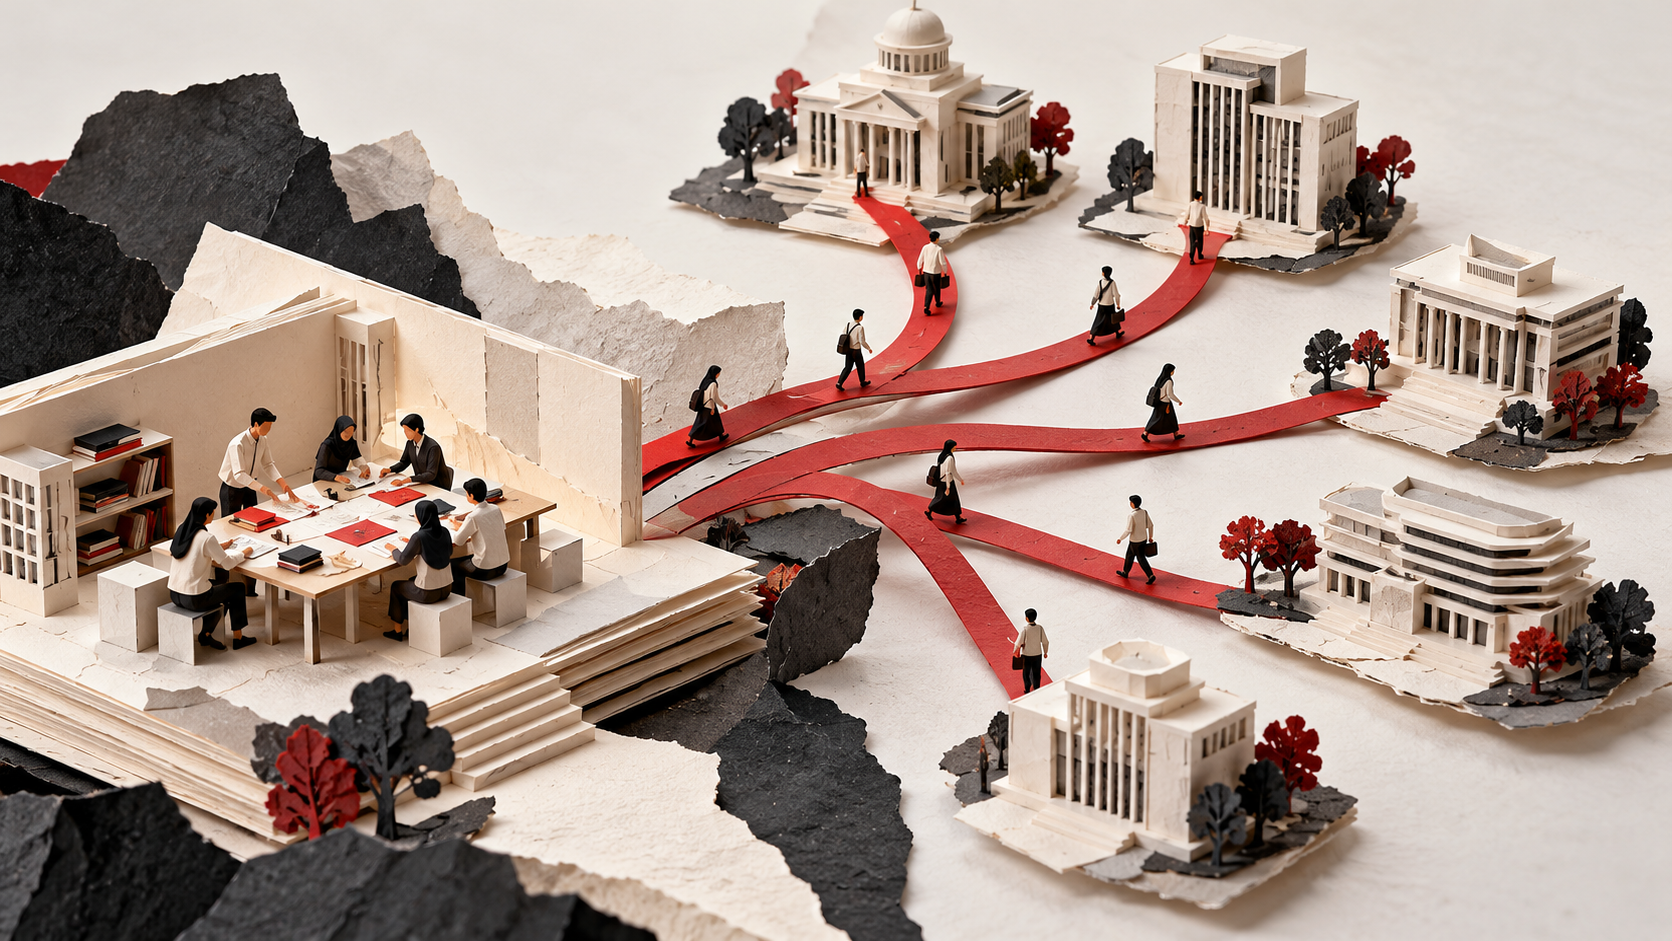
That question matters as governments and organizations expand digital services. On 9 October 2026, Indonesia’s National Civil Service Agency (BKN) and National Cyber and Crypto Agency (BSSN) announced an agreement to place graduates of Politeknik Siber dan Sandi Negara across six government institutions. The initiative is intended to match cyber-skilled graduates with institutional needs and support the reliability and security of digital public services.
The announcement highlights an important workforce lesson: developing talent and deploying talent are two different jobs. Education builds the foundation. Organizations must then give people the right responsibilities, context and opportunities to apply what they have learned.
From classroom knowledge to operational judgment
Cybersecurity is a broad profession, not a single job description. A security operations analyst, penetration tester, incident responder and security governance specialist may all work in the same field, but their daily decisions are very different.
A useful training pathway therefore begins with the work that needs to be done. It defines the capabilities required for a role, gives learners realistic opportunities to practise them and assesses whether they can apply those skills under pressure.
For organizations building a cybersecurity talent pipeline, three elements deserve particular attention:
-
Role-based learning: Connect courses to actual responsibilities, such as log analysis, vulnerability assessment, incident triage or risk reporting.
-
Practical exercises: Use simulated incidents and realistic technical tasks to test decision-making, documentation and collaboration.
-
Structured placement and mentoring: Give new professionals clear responsibilities, supervision and feedback as they move into operational teams.
The distinction is important. Knowing the definition of a security incident is useful. Knowing what evidence to preserve, whom to notify and how to communicate the business impact is more useful when the alert arrives at 2 a.m.
A workforce needs a pathway, not just a certificate
International workforce initiatives are also putting greater emphasis on helping people understand how different cybersecurity careers fit together. The US National Institute of Standards and Technology (NIST), for example, is preparing Cybersecurity Career Week for 19–24 October 2026, with resources and activities designed to help students and career changers explore roles and build career pathways.
For employers, the same principle applies internally. Training should connect to workforce planning: which capabilities are missing, which teams need them and how will performance be evaluated after training?
A practical development plan can include:
-
Assess the gap. Identify the difference between current capability and the requirements of each role.
-
Train against realistic tasks. Combine technical foundations with scenarios drawn from the organization’s operating environment.
-
Measure applied performance. Evaluate how learners investigate, prioritize, document and communicate, rather than relying only on course completion.
-
Build the next step. Use mentoring, supervised assignments and advanced learning to support continued development.
This approach also helps organizations make better use of people moving into cybersecurity from IT support, software development, engineering or other fields. Their previous experience can be valuable, provided the training pathway makes the missing cybersecurity skills explicit.
Turning learning into readiness
For Indonesia’s digital transformation, the challenge is not simply to produce more people who have studied cybersecurity. It is to help institutions build teams that can protect real systems, understand operational priorities and keep learning as threats and technologies change.
That is where structured education matters. ITSEC Cyber & AI Academy supports the development of cybersecurity and AI capabilities through learning designed to connect knowledge with practical professional needs. For individuals, this can help create a clearer path from learning to work. For organizations, it reinforces the importance of treating talent development as an ongoing capability, rather than a one-off training event.
Ready to build practical cybersecurity and AI skills? Explore learning opportunities at ITSEC Cyber & AI Academy.
References
-
Badan Kepegawaian Negara (BKN), “BKN – BSSN Kolaborasi Tempatkan Kompetensi ASN di Bidang Siber Dukung Layanan Digitalisasi Pemerintah di Berbagai Instansi,” 9 October 2026. https://www.bkn.go.id/bkn-bssn-kolaborasi-tempatkan-kompetensi-asn-di-bidang-siber-dukung-layanan-digitalisasi-pemerintah-di-berbagai-instansi/
-
National Institute of Standards and Technology (NIST), “Celebrate Cybersecurity Awareness Month: Spark Your Cyber Career!,” 5 October 2026. https://www.nist.gov/news-events/news/2026/10/celebrate-cybersecurity-awareness-month-spark-your-cyber-career