Logo
Cybersecurity

Security Teams Need to Understand How Software Actually Gets Shipped

Finding vulnerabilities still matters. Preventing weak code, dependencies and configurations from reaching production requires a different set of skills.

ITSEC AsiaITSEC Asia
|
Okt 05, 2026
Security Teams Need to Understand How Software Actually Gets Shipped

A security professional reviews an application and finds a vulnerability. The development team fixes it. Everyone moves on.

Then the same type of problem appears in the next release.

That’s usually a clue that the weakness lives somewhere deeper than one piece of code. Perhaps the build process accepts an unsafe dependency. A security check happens too late. A container configuration is copied from an old template. Developers receive feedback after the release is practically finished.

NIST’s National Cybersecurity Center of Excellence is putting more attention on exactly this part of software security. Its updated DevSecOps resources, published on 24 September, include CI/CD pipeline automation, containerized application deployment and functional scenarios showing security activities throughout the software development lifecycle. NIST

The workforce implication is straightforward. Application security professionals increasingly need to understand how software moves from a developer’s machine into production.

Security Work Is Moving Into the Pipeline

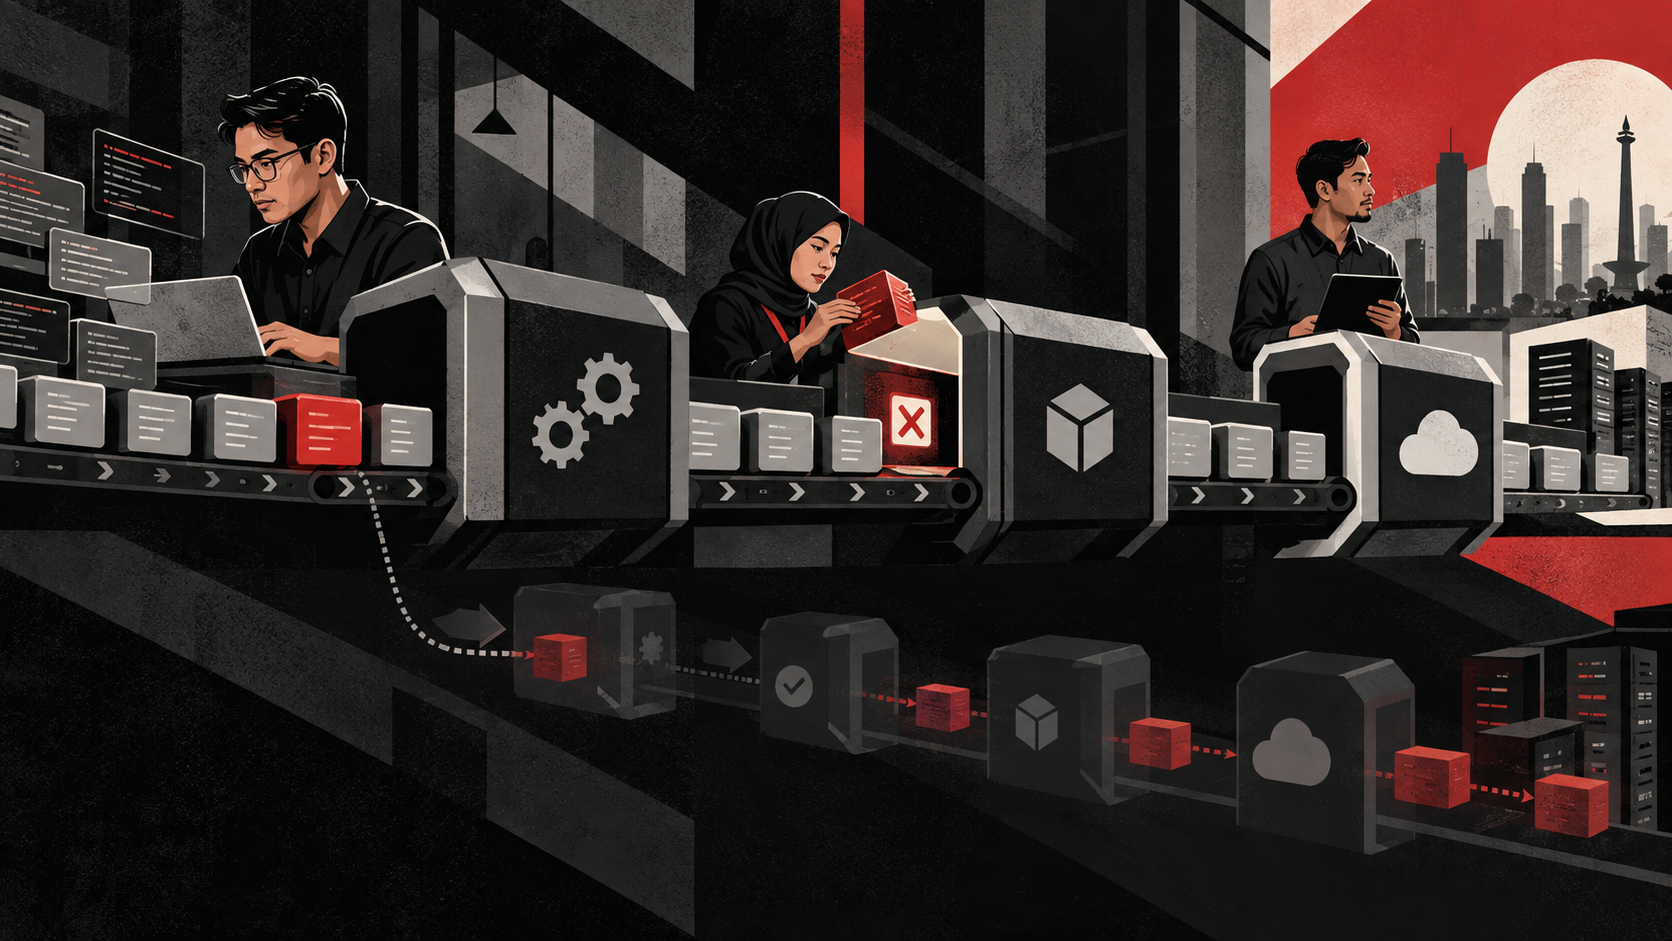
Traditional security testing can happen near the end of development. DevSecOps pushes security activities into the processes developers already use to build, test and deploy software.

That requires people who can work across disciplines.

Useful DevSecOps capability includes understanding:

  • How source code moves through a CI/CD pipeline
  • Where automated security testing should occur
  • How dependencies and software components are tracked
  • How containers and deployment configurations are built
  • Which findings should block a release and which require review
  • How credentials and secrets are handled during builds
  • How security feedback reaches developers quickly enough to be useful

NIST’s DevSecOps project maps practices from its Secure Software Development Framework into a reference model intended to show how security tasks can operate within modern development pipelines. NCCoE

NICE has also added DevSecOps as a formal competency area in version 2.2.0 of its cybersecurity workforce framework. NIST

That puts software delivery knowledge squarely inside cybersecurity skills development.

Automation Still Needs Judgment

A pipeline can run dozens of checks before software reaches production. That doesn’t mean every alert deserves to stop a release.

Someone still has to understand context.

A vulnerable component might be unreachable in the application. Another finding may expose an internet-facing function handling sensitive information. A failed configuration test could indicate a minor deviation or a serious exposure.

The security professional needs enough development knowledge to discuss the finding with engineers and enough risk judgment to decide what deserves immediate attention.

Otherwise, automation simply produces security findings at machine speed. The backlog will be delighted.

Train With the Pipeline Running

DevSecOps is difficult to learn from diagrams alone.

A stronger exercise gives participants source code, a CI/CD pipeline, automated tests, container builds and a deployment environment. Introduce an insecure dependency or configuration, then ask learners to identify where the control should catch it and what should happen next.

Let them change the pipeline, run another build and see the result.

That practical loop fits the learning approach at ITSEC Cyber & AI Academy. Cybersecurity professionals can build technical capability around application security, testing and secure delivery by working with systems that behave like the environments they’ll encounter on the job.

A vulnerability report tells a team what went wrong once.

DevSecOps skills help them change the process that allowed it through.

Explore hands-on cybersecurity and AI learning at ITSEC Cyber & AI Academy.

References

  1. NIST NCCoE, “New NIST NCCoE Resources on DevSecOps and October 28 Webinar on Agentic AI,” 24 September 2026
  2. NIST NCCoE, “Secure Software Development, Security, and Operations (DevSecOps) Practices Live Document,” 24 March 2026, updated on a rolling basis
  3. NIST NICE, “NICE Releases NICE Framework Components v2.2.0,” 28 April 2026
Share this post

You may also like

Your Incident Response Team Has an AI Problem to Rehearse
Cybersecurity

Your Incident Response Team Has an AI Problem to Rehearse

An AI assistant connected to internal data starts returning information it shouldn’t reveal. What does the incident responder collect first? Traditional evidence still matters, but the investigation may also require prompts, model outputs, retrieval sources, system instructions, access permissions and records of actions taken through connected tools. Disabling an endpoint won’t necessarily answer what the model accessed or what information it produced. Recent workforce data suggests many teams haven’t rehearsed that situation. ISACA’s 2026 State of Cybersecurity research, based on more than 1,800 cybersecurity professionals globally, found that only 8% of organizations regularly conduct AI specific response exercises. The same research found that 45% see LLM SecOps as a skills gap, up 12 percentage points from 2025 and 21 points from 2024. ISACA [https://www.isaca.org/about-us/newsroom/press-releases/2026/only-8-percent-of-organizations-global-enterprises-conduct-regular-ai-specific-response-exercises?utm_source=chatgpt.com] AI security is becoming operational work rather quickly. AI CHANGES THE EVIDENCE NIST convened an AI Incident Management Workshop in May because a new class of incidents is emerging as AI systems become embedded in critical infrastructure, cybersecurity and other operational environments. Its work covers incident definitions, lifecycles, taxonomies, existing playbooks

ITSEC AsiaITSEC Asia
|
Okt 07, 2026 — 3 minutes read
AI Penetration Testing vs Traditional Penetration Testing: What's the Difference?
Cybersecurity

AI Penetration Testing vs Traditional Penetration Testing: What's the Difference?

Organizations today face an increasingly complex threat landscape. New vulnerabilities emerge daily, attack surfaces expand continuously and attackers are leveraging automation to move faster than ever before. For many years, traditional penetration testing has been an essential part of cybersecurity programs. However, as environments become more dynamic, many organizations are exploring how artificial intelligence can enhance security assessments and provide more continuous visibility. This shift has given rise to AI penetration testing. But how does AI powered penetration testing compare to traditional penetration testing? Is AI replacing ethical hackers, or are the two approaches designed to work together? UNDERSTANDING TRADITIONAL PENETRATION TESTING Traditional penetration testing involves security professionals simulating real world attacks to identify vulnerabilities and weaknesses before attackers can exploit them. HOW TRADITIONAL PENETRATION TESTING WORKS A typical penetration testing engagement may include: * Reconnaissance and information gathering. * Vulnerability identification. * Exploitation and attack path analysis. * Privilege escalation testing. * Manual validation of findings. * Reporting and remediation recommendations. Traditional penetration testing provides deep insights into an organization's security posture

ITSEC AsiaITSEC Asia
|
Jun 15, 2026 — 5 minutes read
Cybersecurity Training Needs More Room for Failure
Cybersecurity

Cybersecurity Training Needs More Room for Failure

A cybersecurity exercise where everything goes according to plan is wonderfully reassuring. It may also be slightly suspicious. Real incidents rarely arrive with tidy instructions. An alert can look harmless until it isn’t. Evidence can contradict itself. Someone makes an assumption, spends 20 minutes following it and discovers they were looking in entirely the wrong place. That messy part of cybersecurity deserves a bigger role in how people are trained. NIST’s National Initiative for Cybersecurity Education (NICE) is putting that idea directly into its workforce discussion. Its upcoming September session on preparing students for cyber careers focuses on realism-based training, including how controlled failure can become useful workforce data rather than something educators simply mark wrong. That’s a useful distinction. A score tells you whether someone found the answer. Watching how they reached it tells you much more. A WRONG ANSWER CAN REVEAL THE REAL SKILLS GAP Imagine two SOC trainees investigating the same suspicious activity. Both eventually identify the threat. One gets there systematically. The other clicks through five theories, misses a

ITSEC AsiaITSEC Asia
|
Sep 04, 2026 — 3 minutes read

Receive weekly
updates on new posts

Subscribe