Logo
Cybersecurity

Your Cybersecurity Skills Gap Might Be a Job Design Problem

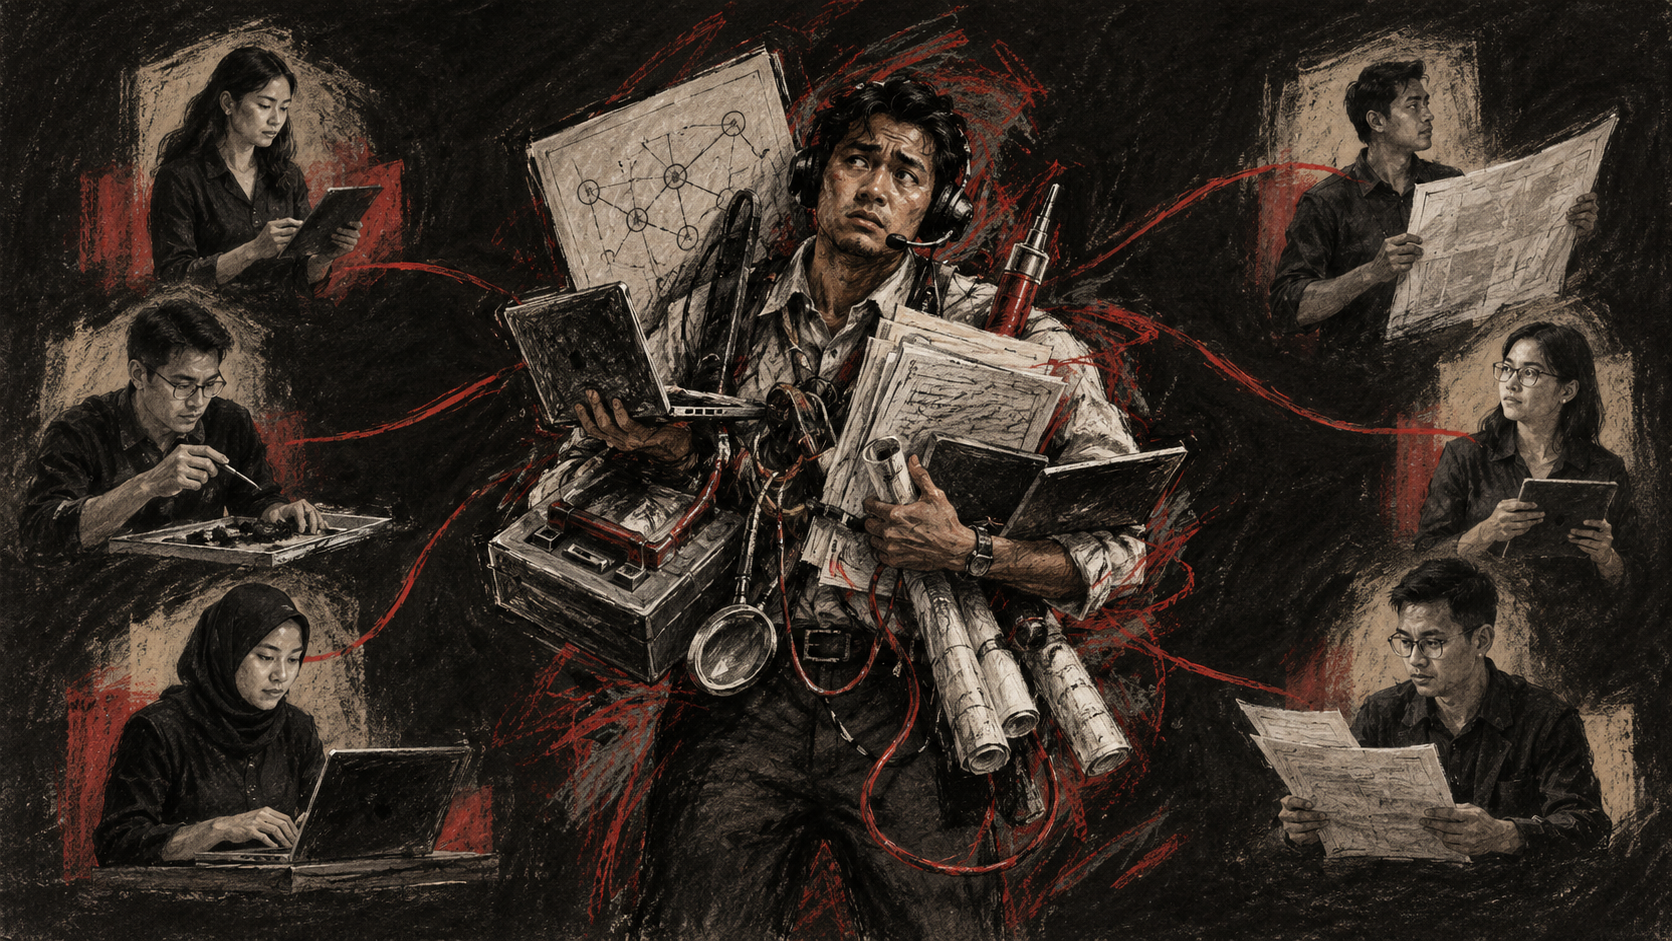
If one vacancy asks for incident response, cloud architecture, penetration testing, compliance and threat intelligence, finding the right candidate may not be the real problem.

ITSEC AsiaITSEC Asia
|
Sep 22, 2026
Your Cybersecurity Skills Gap Might Be a Job Design Problem

Cybersecurity job descriptions can become ambitious documents.

An organization needs someone who understands cloud security, investigates incidents, tests applications, manages risk, explains regulations, tunes security tools and perhaps briefs senior management when something goes wrong.

Five years of experience preferred.

The candidate sounds excellent. Finding this person may take a while.

ENISA’s European Cybersecurity Skills Framework offers a useful reminder that cybersecurity isn’t one profession wearing several different badges. The framework separates the field into 12 professional profiles, including Cyber Incident Responder, Cybersecurity Architect, Penetration Tester, Cybersecurity Risk Manager, Digital Forensics Investigator and Cyber Threat Intelligence Specialist.

Each profile has different tasks, knowledge and competencies. They also depend on one another.

That changes how organizations should think about a “skills shortage.”

Check the Job Before Blaming the Talent Pool

Some roles will naturally overlap, particularly in smaller teams. ENISA’s own user manual treats the framework as flexible and shows how organizations can combine responsibilities according to their circumstances.

The problem starts when overlap becomes accumulation.

A useful workforce review can ask:

  • Which tasks genuinely need to sit with this role?
  • Which capabilities belong elsewhere in the team?
  • Which skills are essential on day one and which can be developed?
  • Where does this person depend on an architect, responder, tester or risk specialist?
  • Are we hiring one role or quietly describing three?

That last question can save a surprising amount of recruitment time.

Cybersecurity Works as a System of Roles

ENISA places its 12 profiles across a management cycle covering planning, implementation, operations and improvement. Strategy, architecture and risk sit around planning. Implementation and education turn plans into capability. Incident response, forensics and threat intelligence support operations. Penetration testing, research and audit help organizations find weaknesses and improve.

The model makes interdependency visible.

A penetration tester can find a weakness, but someone must decide how it affects risk. An architect may redesign the control. An implementer has to deploy the change. Later, an auditor may need to verify that it works.

Expecting one person to perform every step doesn’t necessarily create an efficient team. Sometimes it creates a very long Tuesday.

Training Gets Better When Roles Get Clearer

Clearer role design also makes development more precise.

Instead of sending the entire security function through the same curriculum, organizations can map training to actual responsibilities. Incident responders can practise investigation and containment. Penetration testers can deepen application, API and infrastructure testing. Architects can work through secure design decisions. Risk professionals can practise translating technical findings into business consequences.

ENISA says the ECSF is intended to help HR teams and non-specialists with resource planning, recruitment and career development, while also helping training providers connect learning with workplace requirements.

That same principle fits practical learning at ITSEC Cyber & AI Academy. Hands-on development becomes more useful when the target capability is defined first, then practised through scenarios relevant to the participant’s role.

Cybersecurity still needs more skilled people.

It could also use fewer vacancies looking for one person who apparently contains an entire security department.

Explore practical cybersecurity and AI training at ITSEC Cyber & AI Academy.

References: ENISA: European Cybersecurity Skills Framework, updated 21 September 2026 · ENISA: ECSF Role Profiles · ENISA: ECSF User Manual
Share this post

You may also like

Cybersecurity Careers Should Start Before University
Cybersecurity

Cybersecurity Careers Should Start Before University

Ask a teenager what jobs exist in technology and you’ll probably hear programmer, software engineer or perhaps data scientist. Ask about cybersecurity and the picture can become considerably fuzzier. Maybe “hacker” makes an appearance, usually wearing an imaginary hoodie. That perception matters because Indonesia needs a much larger pool of people who see cybersecurity as a realistic career before they have to choose one. Komdigi has started pushing cybersecurity education further down the talent pipeline. In May, its Digital Human Resources Development Agency provided Basic Cyber Security training to 124 students at SMKN 2 Depok, covering digital security awareness and preparation for a technology-driven workplace. The direction is also appearing internationally. NIST’s NICE program updated its September webinar on 2 September with a specific focus on preparing students for future cyber careers. One part examines how K–12 education can introduce skills connected to immediate workforce realities such as cloud security and generative AI. Cybersecurity education is moving earlier because the work itself isn’t waiting. EXPOSURE BEFORE SPECIALISATION Starting earlier doesn’t mean asking

ITSEC AsiaITSEC Asia
|
Sep 07, 2026 — 3 minutes read
Supply Chain Attacks Are Growing: Why Third-Party Risk Needs Continuous Testing
Cybersecurity

Supply Chain Attacks Are Growing: Why Third-Party Risk Needs Continuous Testing

Introduction Third-party involvement in data breaches doubled from 15 percent to 30 percent in a single year, the largest one-year shift ever recorded in the Verizon 2025 Data Breach Investigations Report. That is not a gradual trend line, it is a structural shift in how attackers reach their targets. Rather than breaching a company directly, they go after the vendor, the software dependency, or the service provider sitting quietly inside that company's trust boundary. As Indonesia's leading cybersecurity company, ITSEC Asia works with organizations across finance, healthcare, and technology who are only now realizing that their own defenses were never the whole picture, because a breach can start three vendors away and still land squarely on their desk. Source: Supply Chain Attack Statistics 2026, Stingrai Research · Supply Chain Attack Statistics for 2026, Swif The Numbers Behind the Shift A supply chain compromise now costs an average of 4.91 million US dollars and takes 267 days to identify and contain, the longest lifecycle of any breach vector tracked in IBM's Cost

ITSEC AsiaITSEC Asia
|
Jul 31, 2026 — 4 minutes read
Cybersecurity Indonesia: Rising Cyber Threats and the Importance of a Strong Digital Security Strate
Cybersecurity

Cybersecurity Indonesia: Rising Cyber Threats and the Importance of a Strong Digital Security Strate

cybersecurity indonesia
cyber security indonesia
cybersecurity di indonesia
cyber security di indonesia
cybersecurity in indonesia
cyber security in indonesia

Indonesia is facing a growing risk of ransomware attacks, phishing campaigns, data breaches and digital infrastructure exploitation that can impact business operations, public services and customer trust. In recent years, sectors including government, financial services, manufacturing, education and digital platforms have become major targets of cyber attacks. As one of the leading cybersecurity companies in Indonesia, ITSEC Asia provides cybersecurity services designed to help organizations strengthen cyber resilience and protect against evolving digital threats. -------------------------------------------------------------------------------- WHY CYBERSECURITY INDONESIA HAS BECOME A NATIONAL PRIORITY Cybersecurity Indonesia is no longer just a technical concern. Cybersecurity has become a critical component of business resilience and national digital security. Indonesia’s fast-growing digital economy is driving organizations to adopt new technologies at a rapid pace. At the same time, cyber threats continue to evolve through: * Ransomware attacks targeting organizations * Customer and sensitive data breaches * AI-powered phishing and social engineering * Cloud infrastructure attacks * Web and mobile application exploitation * Threats against critical infrastructure Organizations across Indonesia are increasingly recognizing that cyber attacks are

ITSEC AsiaITSEC Asia
|
Mei 07, 2026 — 4 minutes read

Receive weekly
updates on new posts

Subscribe