Logo
Cybersecurity

Your SOC Can’t Handle a Cyber Crisis Alone

The technical team may find the incident first. What happens next quickly becomes everybody else’s problem too.

ITSEC AsiaITSEC Asia
|
Sep 15, 2026
Your SOC Can’t Handle a Cyber Crisis Alone

Imagine a ransomware incident at 10:30 on a Tuesday morning.

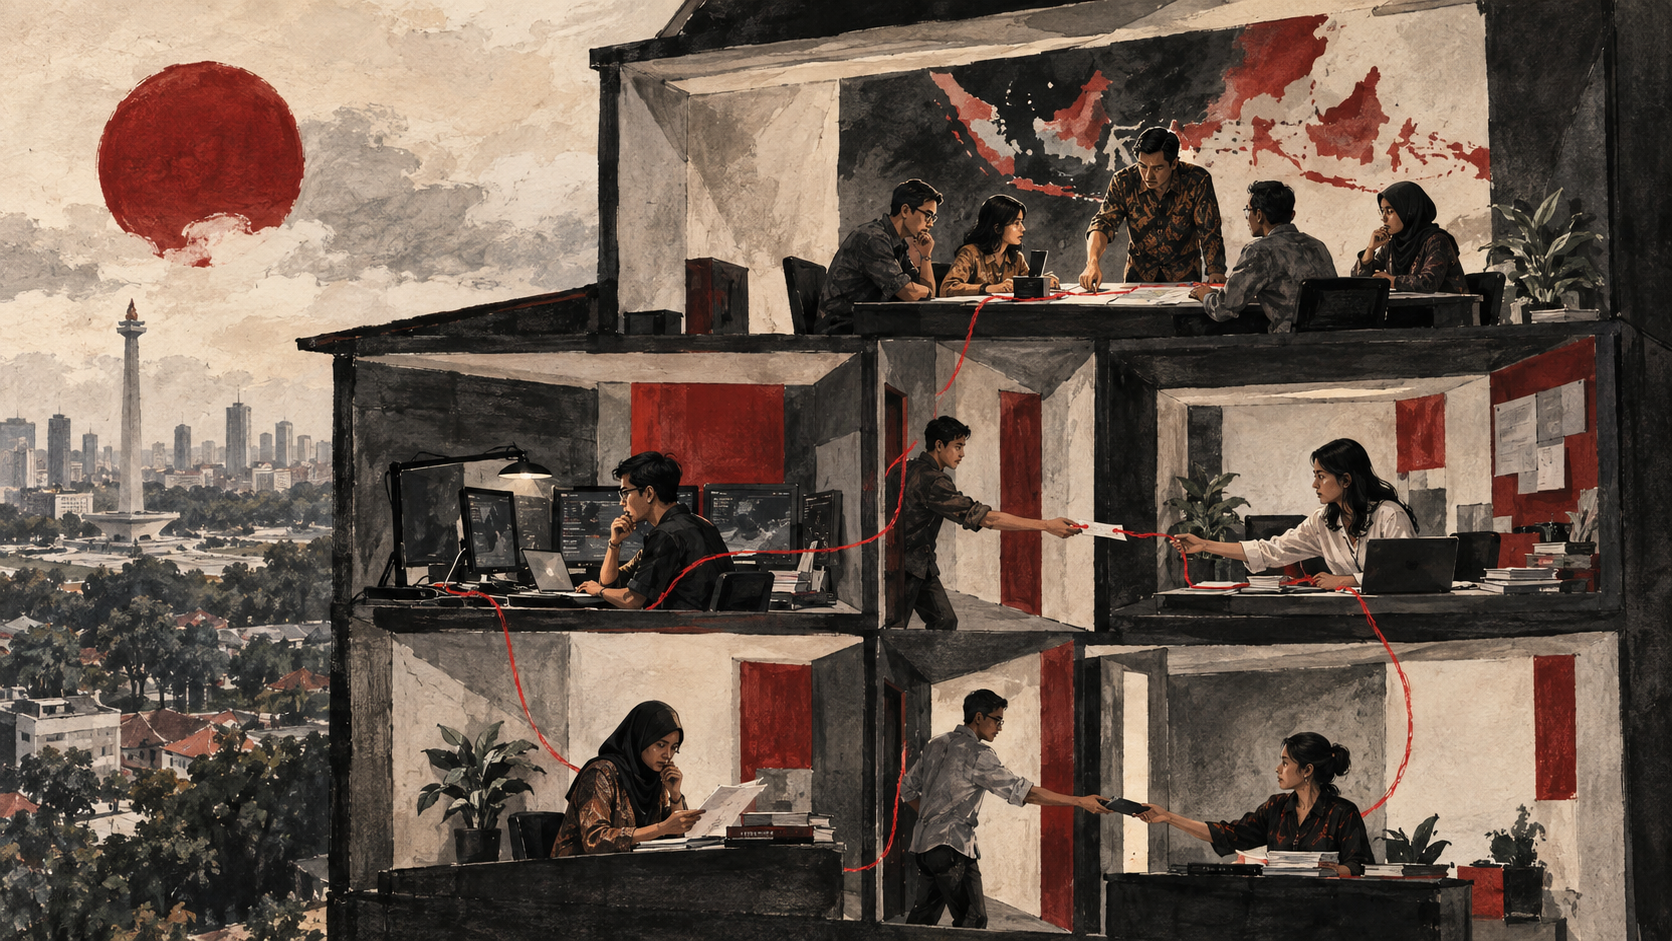
The SOC detects suspicious activity and starts investigating. Soon IT needs to isolate systems. Management wants to know whether operations should continue. Legal needs facts. Communications may need to prepare a response. Someone has to decide whether customers or authorities need to be informed.

By lunch, cybersecurity has become an organizational exercise.

That reality is reflected in current training from the International Telecommunication Union. An ITU Academy incident response course currently open for applications uses three scenarios: a ransomware attack, a data breach and an attack affecting a national education system. Participants work through the incident response lifecycle using collaborative tabletop exercises.

The lesson is useful far beyond education. Incident response capability depends on how well different people can make decisions together.

Technical Skill Is Only One Layer

A strong SOC can identify malicious activity, analyse evidence and recommend containment. It still needs an organization around it that knows what happens next.

Useful incident response capability therefore spreads across several functions:

  • SOC and security teams investigate, contain and preserve evidence.
  • IT and infrastructure teams understand affected systems and recovery dependencies.
  • Management makes operational and risk decisions with incomplete information.
  • Legal and compliance teams assess regulatory and contractual obligations.
  • Communications teams prepare accurate information for employees, customers or other stakeholders.

None of these groups needs identical cybersecurity expertise.

They do need enough shared understanding to work through the same incident.

ITU’s 2026 Regional CyberDrill for the Americas illustrates that model. The exercise brought together technical and management officials from CIRT, CERT and SOC environments alongside cybersecurity authorities, ministries, regulators and academia. Its objectives included improving technical capability, communication, incident management and coordination.

Tabletop Exercises Reveal Awkward Questions Early

A tabletop exercise is deceptively simple. Give a team a plausible incident and ask what they would do.

Then keep asking questions.

Who can authorize taking a critical system offline? Who contacts the regulator? Can the organization restore the affected service? Who briefs the CEO? What happens if the person who normally approves something is unreachable?

Suddenly the incident response plan starts developing holes.

That’s useful. A simulation can reveal unclear ownership, outdated contact lists, missing escalation paths and assumptions that looked perfectly reasonable inside a document.

ITU’s cyber disaster response training uses this approach explicitly, combining tabletop scenarios with hands on exercises and debriefs to develop communication and decision making during cyber attacks.

Finding those gaps during an exercise is considerably cheaper than discovering them while ransomware is spreading.

Train the Team Around the Technology

Technical cyber range exercises remain valuable, particularly for SOC analysts and incident responders. The next step is connecting those technical exercises with the people who have to act on their findings.

A realistic scenario might begin with analysts investigating suspicious activity, then require a handover to management, an operational decision from IT and a concise briefing for communications.

That type of practice fits naturally within ITSEC Cyber & AI Academy, where scenario based learning can help participants connect technical cybersecurity capability with the coordination and judgment required during real incidents.

The SOC may be the first room where the alarm goes off.

A prepared organization knows what every other room does next.

Explore practical cybersecurity and AI training at ITSEC Cyber & AI Academy.

References: ITU Academy: Incident Response for Secure School Connectivity · ITU: 16th Regional CyberDrill for the Americas, 2026 · ITU Academy: Cyber Disaster Response Simulation Exercises
Share this post

You may also like

Cybersecurity Skills Need Maintenance Too
Cybersecurity

Cybersecurity Skills Need Maintenance Too

A cybersecurity professional completes training on Friday. They’ve worked through the material, passed the assessment and returned to their job with a fresh set of skills. Six months later, the environment looks different. A cloud service has changed. The team has introduced AI tools. Attack techniques have evolved. Someone redesigned the incident process. Three new systems appeared and one old application that was supposedly retiring is, mysteriously, still alive. This is why cybersecurity training increasingly needs to behave less like an annual event and more like professional maintenance. NIST’s FISSEA Fall Forum on 15 September puts that idea into practice. Its agenda includes an interactive session on building a micro training module, followed by examples of cybersecurity learning tied to the NICE Workforce Framework and practical skill application. The format matters. Learning doesn’t always need another full week away from work. SMALL LEARNING CAN SOLVE SPECIFIC PROBLEMS CISA already uses micro learning as part of its cybersecurity training model. Its Continuous Diagnostics and Mitigation program offers short modules of roughly 3 to 10 minutes,

ITSEC AsiaITSEC Asia
|
Sep 14, 2026 — 3 minutes read
How Continuous Pentesting Supports PCI DSS Compliance
Cybersecurity

How Continuous Pentesting Supports PCI DSS Compliance

Organizations that process, store or transmit payment card information face increasing pressure to protect sensitive data and comply with industry standards. Among the most widely recognized requirements is the Payment Card Industry Data Security Standard (PCI DSS). While many organizations view PCI DSS as a compliance exercise, the reality is that the framework is designed to strengthen security and reduce the risk of data breaches. As cyber threats continue to evolve, organizations are also recognizing that point-in-time assessments may no longer provide sufficient visibility. This is where Continuous Pentesting and Continuous Security Validation can help. WHAT IS PCI DSS? PCI DSS is a security framework developed to help organizations protect cardholder data and maintain secure payment environments. It applies to merchants, financial institutions, payment processors and service providers that handle payment card information. The standard covers multiple areas, including: * Network security. * Access control. * Vulnerability management. * Monitoring and logging. * Security testing. * Incident response. The objective is not simply compliance but the protection of sensitive payment information. WHY PENETRATION TESTING

ITSEC AsiaITSEC Asia
|
Jun 15, 2026 — 4 minutes read
Think Your System Is Secure? Penetration Testing Can Prove It
Cybersecurity

Think Your System Is Secure? Penetration Testing Can Prove It

INTRODUCTION Today, almost every organization relies on digital systems to run daily operations, from websites and cloud applications to payment systems and internal databases.  However, as digital infrastructure grows, so do cybersecurity risks. Attackers constantly look for vulnerabilities in applications, networks, and systems that they can exploit to gain unauthorized access or steal sensitive data (Cloudflare, 2024). Because of this growing threat landscape, organizations need ways to test their defenses before real attackers attempt to breach them. One of the most effective methods is penetration testing, often called pen testing, where cybersecurity professionals simulate attacks to identify security weaknesses before malicious actors do (IBM, 2024). In simple terms, penetration testing is authorized hacking designed to improve security rather than cause damage. Source: Cloudflare.com [https://www.cloudflare.com/learning/security/glossary/what-is-penetration-testing/], ibm.com [https://www.ibm.com/think/topics/penetration-testing] WHAT IS PENETRATION TESTING? Penetration testing is a cybersecurity assessment where security experts simulate cyberattacks on systems to identify vulnerabilities that attackers could exploit. These experts that are often known as penetration testers or ethical hackers use techniques similar to real attackers, but with permission from the organization and with the goal

ITSEC AsiaITSEC Asia
|
Apr 02, 2026 — 6 minutes read

Receive weekly
updates on new posts

Subscribe