Logo
Cybersecurity

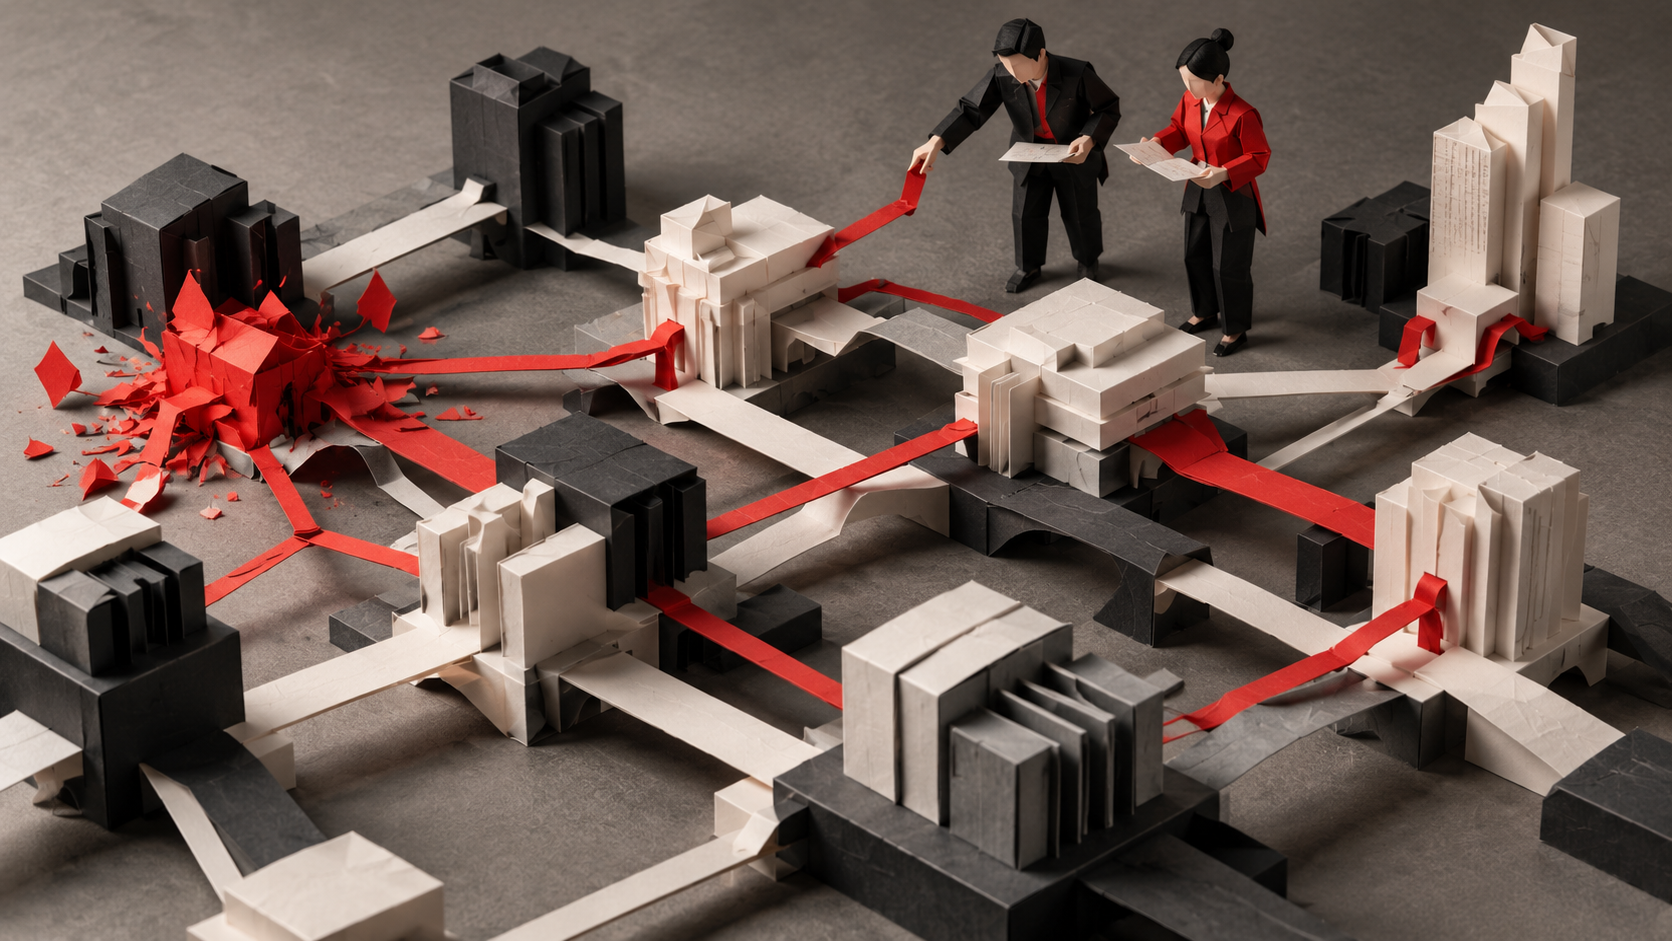
One Compromised System Rarely Stays One Compromised System

Modern incidents travel through dependencies. Security teams need people who can work out where the damage could go next.

ITSEC AsiaITSEC Asia
|
Sep 30, 2026
One Compromised System Rarely Stays One Compromised System

A business application stops working.

The server itself is fine. The network looks normal. Authentication is available. Then someone discovers that an external service used by the application is unavailable.

Suddenly the incident diagram gets bigger.

ENISA’s Threat Landscape 2026, published on 22 September and discussed in a dedicated webinar on 29 September, puts this problem near the centre of its analysis. ENISA says the growing interconnectedness of digital ecosystems is increasing exposure to cyber risk and continues to observe attacks targeting dependencies, including supply chain and third party relationships. ENISA

For workforce development, there’s a practical lesson here: cybersecurity professionals need to understand dependencies as well as assets.

An Asset List Doesn’t Show the Whole Risk

Knowing what systems an organization owns is useful.

Knowing what those systems rely on is different.

A customer portal might depend on an identity provider, DNS, cloud infrastructure, payment service, API, software library and managed service. Several other applications may rely on exactly the same components.

Compromise one shared dependency and the blast radius changes quickly.

Security teams therefore need skills to identify:

  • Which external services support critical business functions
  • Which applications share the same infrastructure or provider
  • Where software and data originate
  • Which dependencies have privileged access
  • What happens if a dependency becomes unavailable
  • Which alternative processes exist when a service fails
  • Who owns the relationship when investigation or recovery is required

The last question has a habit of becoming surprisingly difficult at 2 a.m.

Incident Response Needs a Dependency View

Dependency knowledge changes how people investigate incidents.

Suppose unusual activity appears in three applications simultaneously. Looking at each application separately may produce three investigations. Knowing that all three depend on the same identity service immediately creates another hypothesis.

The same principle applies to recovery.

Restoring a server doesn’t restore a business process if a required external service remains unavailable. A technically healthy application may still be unusable because its authentication, API or data provider has failed.

ENISA reports that 73% of organizations targeted in the incidents it analysed were entities classified as essential or important under NIS2. Its analysis also says cyber dependencies can increase the scale and impact of incidents across interconnected infrastructure. ENISA

Cyber resilience therefore requires people who can reason across organizational boundaries.

Put Dependencies Into the Exercise

Training can make this capability visible.

Give learners a simulated organization containing several applications, shared infrastructure and external services. Provide the architecture, but don’t reveal every dependency.

Then trigger an incident at one supplier.

Participants must discover which services rely on it, determine what evidence is available, assess business impact and decide which teams or external parties need to be involved.

A more difficult version introduces a recovery decision that fixes one system while breaking another dependency.

This type of scenario fits practical learning at ITSEC Cyber & AI Academy, where cyber range exercises can connect technical investigation with architecture, incident response and operational decision making.

Security teams already ask, “What happened?”

The next useful question is often, “What else depends on it?”

Explore practical cybersecurity and AI training at ITSEC Cyber & AI Academy.

References: ENISA Threat Landscape 2026, 22 September 2026 · ENISA: How Dependencies Weaken Digital Resilience · ENISA Threat Landscape Webinar, 29 September 2026
Share this post

You may also like

AI Is Raising the Bar for Cybersecurity Talent
Cybersecurity

AI Is Raising the Bar for Cybersecurity Talent

For cybersecurity teams, AI is quickly moving from something experimental to something people actually use. The World Economic Forum’s Global Cybersecurity Outlook 2026 found that 77% of surveyed organizations had adopted AI for cybersecurity. It is already being used for tasks such as phishing detection, intrusion response and user-behaviour analysis. That sounds like good news for teams struggling with workload. And mostly, it is. But AI doesn’t remove the need for skilled cybersecurity professionals. It changes what those professionals need to be good at. AUTOMATION CAN DO MORE. SO HUMANS HAVE TO DO MORE TOO. The same WEF research found that 54% of organizations considered insufficient knowledge or skills a barrier to using AI effectively in cybersecurity. Another 41% pointed to the need for human oversight. That second number matters. AI can analyse enormous amounts of information quickly. What it still struggles with is context: whether an unusual event is genuinely dangerous, how a technical issue affects the business and what action makes sense when the available information is incomplete. Cybersecurity professionals increasingly need

ITSEC AsiaITSEC Asia
|
Sep 02, 2026 — 3 minutes read
Data Protection and Cybersecurity Laws in the Asia-Pacific Region
Cybersecurity

Data Protection and Cybersecurity Laws in the Asia-Pacific Region

Info

Apart from sales and trade, the majority of internet users utilize it for socializing and interacting with peers online. For instance, there were 3.8 billion social media users in January 2020, which represents a 9 percent increase from the previous year. The advancements in internet and related communication technologies enable easy access to information from anywhere on the planet. For example, an online merchant operating in Thailand can offer their services to customers residing in the European Union and the United States. In order to address the dissemination of personal information, including financial, medical, and other types of personal data, worldwide through the internet, appropriate legal regulations need to be established to protect the personal data of citizens and the digital assets of organizations while working online. Following the implementation of the General Data Protection Regulation (GDPR) in the European Union (which came into effect on May 25, 2018), which governs data protection and privacy in EU countries and regulates the transfer of personal data outside the European Union and

ITSEC AsiaITSEC Asia
|
Jul 10, 2023 — 11 minutes read
OWASP Top 10 Explained: The Risks Every Organization Should Understand
Cybersecurity

OWASP Top 10 Explained: The Risks Every Organization Should Understand

Modern applications have become increasingly interconnected and complex. Organizations rely on web applications, APIs and cloud services to support critical business operations and deliver digital experiences. Unfortunately, attackers are evolving just as quickly. As cyber threats continue to grow, understanding common application security risks has become essential. This is where the OWASP Top 10 plays an important role. Widely regarded as one of the most influential resources in application security, the OWASP Top 10 provides organizations with a practical framework for understanding and prioritizing the most critical risks affecting web applications. Whether you are a developer, security professional or business leader, understanding these risks is essential for building stronger cyber resilience. WHAT IS OWASP? OWASP, or the Open Worldwide Application Security Project, is a global non-profit organization focused on improving software security. Among its many initiatives, the OWASP Top 10 is perhaps the most widely recognized. It highlights the most significant security risks affecting modern web applications based on industry data and expert consensus. The list is not intended to be a compliance checklist. Instead,

ITSEC AsiaITSEC Asia
|
Jun 15, 2026 — 5 minutes read

Receive weekly
updates on new posts

Subscribe